The FlyDubai axe attack raises urgent questions about detecting lone actors who hold trusted access, lack organizational ties, and evade traditional intelligence, demanding better integration, AI, and deeper allied cooperation.
Strategy Demands Choosing Among Threats
At the Richard Nixon Foundation’s Grand Strategy Summit in Washington, Sebastian Gorka, White House Deputy Assistant to the President and Senior Director for Counterterrorism, highlighted a fundamental principle of national security strategy: strategy requires choices. A government can identify dozens of dangers, but it cannot treat all of them as equally important. “Strategy” means determining which threats most directly affect vital national interests and concentrating intelligence, resources, technology and political attention against them.
That principle is particularly relevant to the Trump administration’s 2026 US Counterterrorism Strategy. The strategy puts the protection of Americans at the center of the mission, concentrates American capabilities against the most dangerous terrorist threats, emphasizes technological advantage, and calls on capable allies and partners to assume greater responsibility. This is a strategy built around prioritization. But it raises a harder question: What happens when the terrorist threat changes faster than the institutions designed to detect it?
Lone Wolf Terrorism Defies Traditional Detection
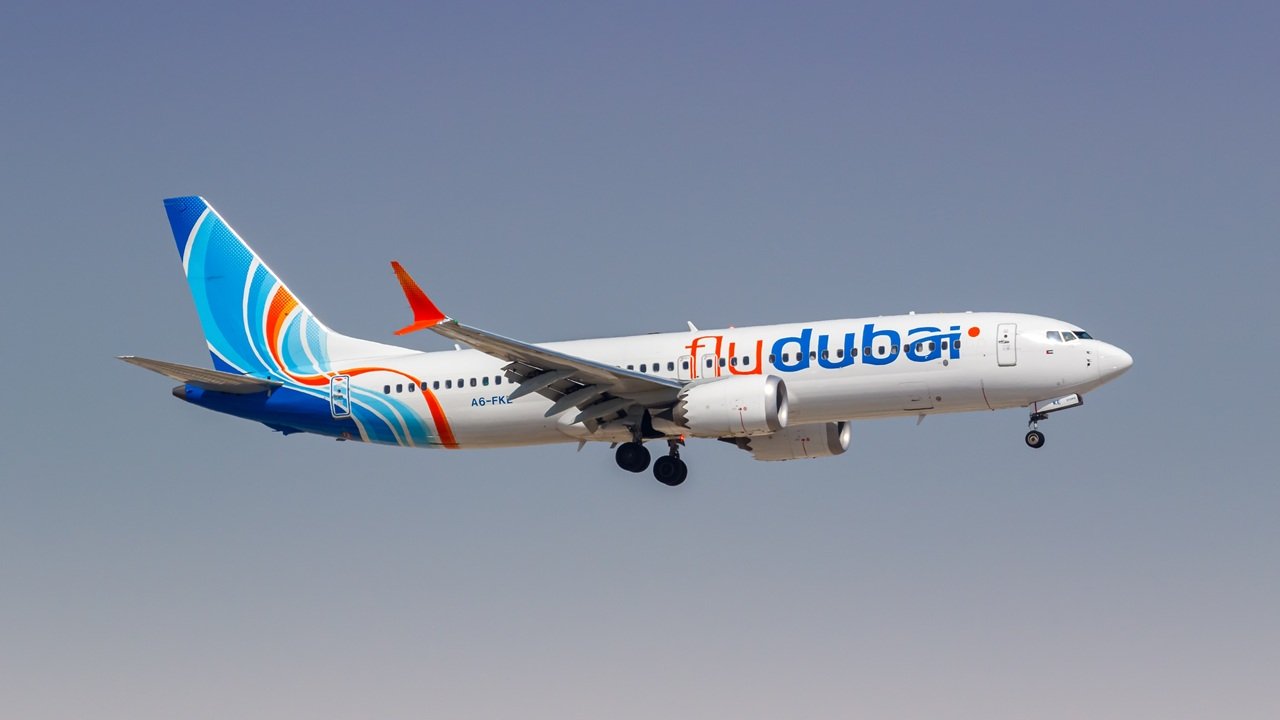
The incident aboard FlyDubai Flight FZ1073 on September 30—in which co-pilot Hamam al-Hammami attacked the pilot with an axe, seized control of the aircraft, and put it into a steep dive before passengers stormed the cockpit and rescued the plane—should force policymakers to confront that question.
Emirati authorities have treated the incident as an attempted terrorist attack; in the days that followed, it was revealed that al-Hammami had been removed from a pilot job at Oman Air after colleagues raised alarm at his extremist views. It is likely no coincidence that the aircraft was bound for Tel Aviv and had 170 people aboard, mostly Israeli citizens. Even so, the ongoing investigation must impartially determine al-Hammami’s motive, whether others were involved, and what warning signs, if any, existed.
Those facts matter, and speculation should not replace them. But the strategic question is already legitimate: How does a government identify a potentially dangerous individual who occupies a trusted position, possesses legitimate access to sensitive infrastructure, remains largely outside traditional counterterrorism intelligence, and may move toward violence without producing the operational footprint normally associated with an organized terrorist plot? How do we defeat that terrorism model?
Connecting Fragmented Signals Across Borders
How Better Intelligence Integration Can Help Defeat Terrorism
The answer is not mass surveillance, nor is it abandoning the counterterrorism architecture developed since September 11. It is adding a new capability to it. The first requirement is to make intelligence integration as important as intelligence collection. Governments already possess enormous quantities of information. The vulnerability increasingly lies in fragmentation. One agency may possess one piece of information, another government a second, and a private institution a third. Separately, they may mean little. Connected, they may reveal a threat. The strategic challenge is therefore to identify relevant signals across institutional and national boundaries.
AI Bolsters Human Analytical Judgment
Artificial intelligence should become central to this effort. AI is not simply another technological instrument in the counterterrorism toolbox. Properly governed, it can strengthen the ability of experienced analysts to process enormous quantities of fragmented information and identify patterns or anomalies that conventional bureaucratic systems may overlook. Human judgment remains indispensable, particularly when fundamental rights and security decisions are involved. But human judgment supported by increasingly sophisticated analytical technology could materially improve how early governments recognize emerging threats. In 21st-century counterterrorism, technological superiority increasingly means intelligence superiority.
Trusted Partners Enable Faster Action
The third requirement is deeper operational cooperation among trusted partners. The emerging threat is inherently transnational. An individual’s travel, employment, communications, contacts and exposure to extremist influence may cross several jurisdictions. Relevant information may therefore exist in several countries, while no single government possesses enough of it to recognize the danger. Washington does not need indiscriminate information-sharing with everyone, but it does need exceptionally strong operational relationships with friendly governments that possess the capabilities, intelligence, and institutional trust required to act together quickly. The objective should be straightforward: connect the information before investigators are forced to reconstruct it after an attack.
Lone Wolf Terrorism Evades Organizational Penetration
This brings us back to Gorka’s argument. Prioritization does not mean doing less for the sake of doing less. It means concentrating national power where it can produce the greatest strategic effect. The Trump administration’s counterterrorism strategy provides important elements of that framework: identifying the threats most dangerous to Americans, maintaining pressure against terrorist organizations capable of external operations, exploiting American intelligence and technological advantages, and transferring greater responsibility to capable partners.
The administration deserves recognition for restoring this strategic discipline. The next step is to apply the same discipline to a terrorist threat that may increasingly emerge outside the organizational structures counterterrorism agencies have become exceptionally skilled at penetrating.
Making the Next Threat Harder to Hide
For years, one of the central questions of counterterrorism was how to penetrate a terrorist organization before it could attack. Policymakers must now confront another question: How do you detect the terrorist when there may be no organization to penetrate? The FlyDubai investigation will establish the facts of one case. But strategy has a responsibility beyond investigating what has already happened. It must identify vulnerabilities before adversaries exploit them.
President Donald Trump and his national-security team have established a framework centered on prioritization, prevention and American strategic advantage. Building upon it will require intelligence integration, technological superiority and deeper cooperation among trusted partners. The objective is not to predict every act of violence—no government can—but to make the next emerging terrorist model progressively harder to conceal and progressively easier to disrupt.